
New Mexico lawmakers confronted state technology officials Monday over a growing gap between the cybersecurity rules on the books and the agencies ignoring them.
The Legislative Finance Committee hearing in Santa Fe laid bare a structural problem: the state has invested in tools and standards, but elected offices — including the state auditor and state treasurer — have declined to comply, citing their independence from the executive branch. KOB 4 reported that Chief Information Security Officer Raja Sambandam told lawmakers some agencies blame a lack of resources, while others simply refuse the oversight.
Sen. Michael Padilla demanded a list of every non-compliant agency, framing the request as pressure to force action. “Where are the holes, like, who is creating a problem for state government,” Padilla said in the meeting. “And then that would be leverage to go to them and say, well here are the 27 or 2,700 things you need to do.”

“You can lead a horse to water, but you can’t make them drink. Now is the time to drink, we’re in a crisis right now, we have several things that are going on worldwide,”
The refusal by the state auditor’s office and the state treasurer’s office to follow Office of Cybersecurity protocols introduces a constitutional friction point. These offices argue their independence from the executive branch shields them from executive-branch mandates. Wisevoter noted this dynamic tests whether centralized security standards can reach beyond the cabinet agencies the governor directly controls.
State Senator George Munoz wants the governor to issue an executive order compelling universal compliance. “Yeah, they need to be, they have to be, this is the world we live in,” Munoz told KOB 4 reporter Blake Troli. “Everybody’s information is vulnerable. But could you imagine if the system was hacked into DOT’s traffic light system and all the lights were red and one time or all green at one time.”
Barreras emphasized that the Department of Information Technology has already procured the necessary cybersecurity toolset. The Office of Cybersecurity sends annual security assessments to every agency highlighting vulnerabilities, yet agencies are not consistently responding to those reports. The gap is not procurement; it is execution.
Sambandam distinguished between agencies citing budget constraints and those citing sovereignty. That distinction matters for the legislature’s next move: appropriations can fix the first, but only a governor’s order — or a court fight — can resolve the second.
The committee did not receive a full roster of non-compliant agencies, nor a precise count of outstanding remediation actions — Padilla’s “27 or 2,700” figure reflects that uncertainty. Whether the governor will issue the executive order Munoz requested, and whether such an order would withstand a legal challenge from the Auditor or Treasurer, are open questions heading into the next legislative session.
Keep reading

Rockets Rout Pacers 119-104 Behind 19 Three-Pointers, Balanced Scoring
The Houston Rockets routed the Indiana Pacers 119-104 on Wednesday night at Gainbridge Fieldhouse, with Kevin Durant scoring...
Teen Wanted in Connecticut Shooting Arrested in Mesa After Two-Month Search
A 17-year-old wanted in a September shooting that critically injured another juvenile in New Haven, Connecticut, was arrested...
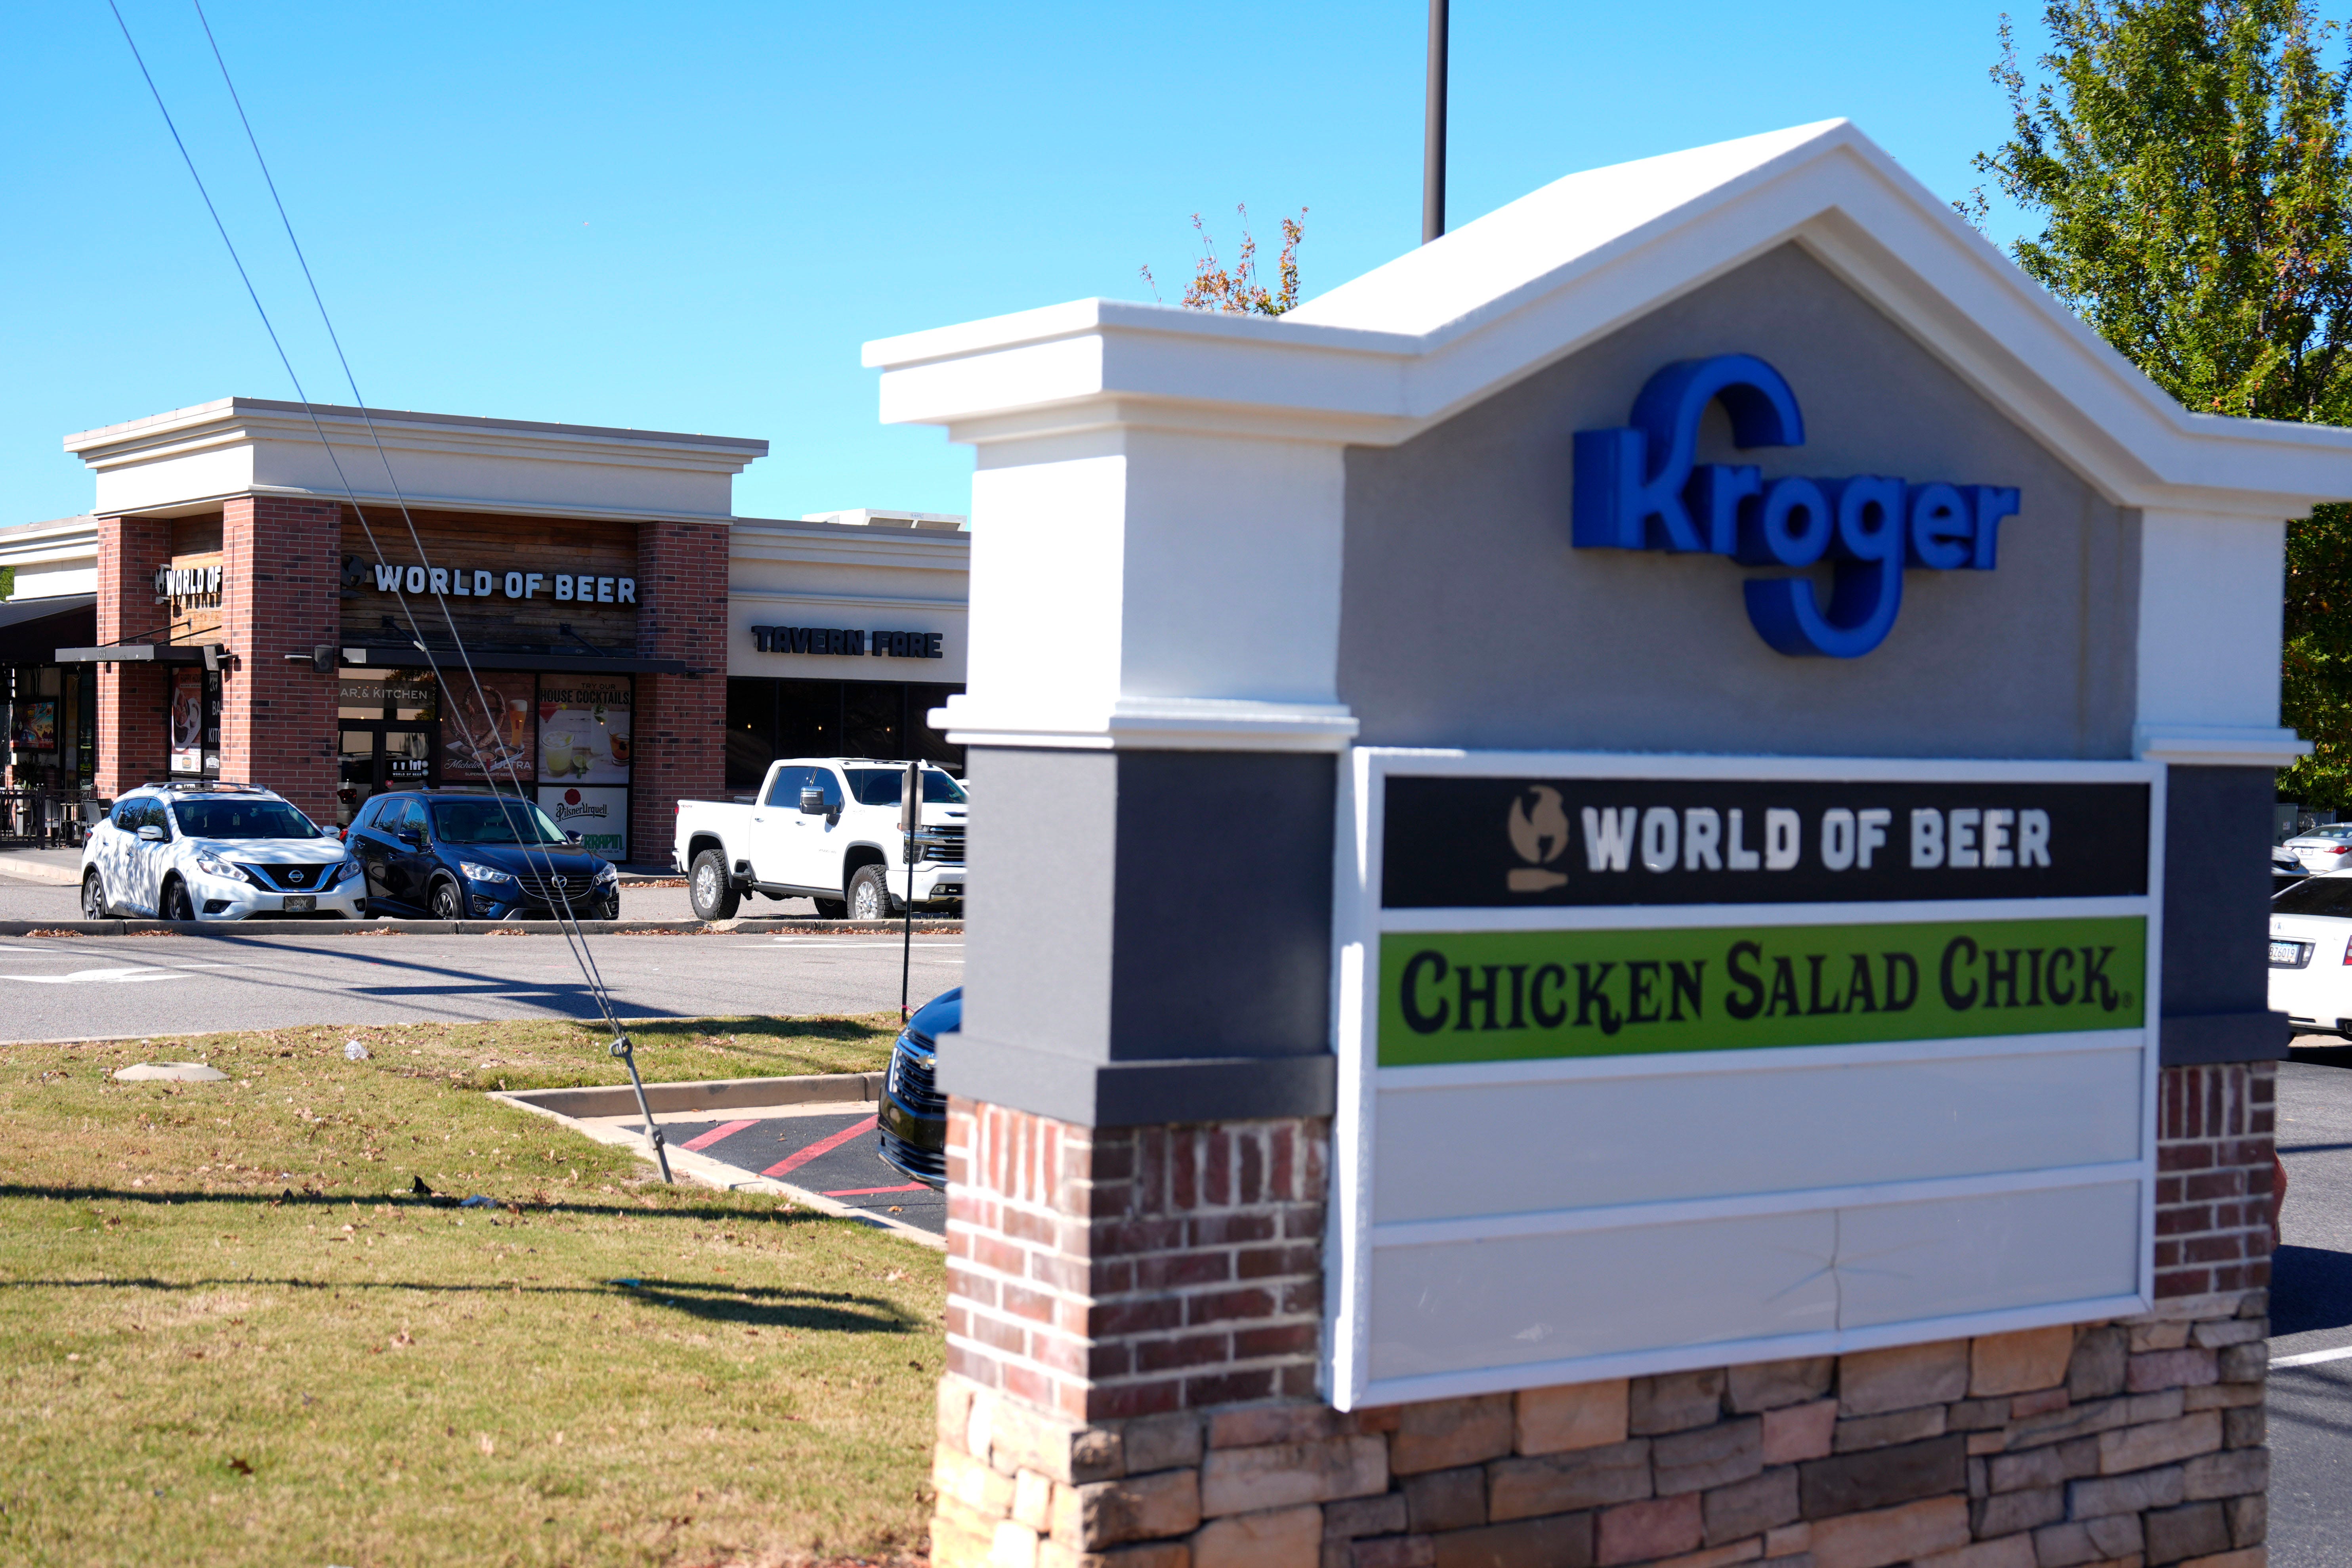
Augusta Chronicle: World of Beer Site Listed in Urgent Care Clinic Plans
Plans filed for an urgent-care clinic at 2819 Washington Road signal the likely end of the World of...
Boston Zoning Commission Adopts New Cleary Square Squares + Streets Zoning to Support Housing and Small Businesses
The Boston Zoning Commission adopted new zoning for Hyde Park's Cleary Square on Wednesday, capping nearly three years...