
School districts across Massachusetts face cyberattacks and data security risks that threaten operations, according to the editorial board of The Boston Globe.
Springfield Public Schools suspended operations for four days in September due to what local officials described as a cyber incident. Sutton also dealt with a cybersecurity problem affecting its school system around the same time, while Milford Public Schools faced a hacking attempt in August that staff successfully thwarted.
These digital breaches follow earlier disruptions across the state, including the 2025 PowerSchool data breach that impacted districts such as Woburn, Westford, and Millis.
The consequences of these digital intrusions extend far beyond simple IT inconveniences. The recent hacking incident in Springfield caused the district to lose email, phone, and computer systems, crippling its ability to operate normally. Administrators found themselves locked out of the tools they rely on for student transportation and meal preparation. Schools had to close because staff lacked access to critical student medical information.
When Springfield Public Schools finally reopened, not all systems were back online, forcing teachers and students to rely on printed materials. Schools remain prime targets for malicious actors because of the sheer volume of sensitive data they store, including students’ medical records, personal information, and household income.
Hackers are usually motivated by financial greed, demanding ransoms to end the digital sieges against entities that typically maintain weaker cybersecurity defenses than private corporations.
Completely preventing all cyber incidents is a nearly impossible task, especially as artificial intelligence grows more powerful and accessible to malicious actors. Given that reality, school officials need to make sure education can continue when attacks happen.
According to Cliff Steinhauer, director of information security and engagement for the National Cybersecurity Alliance, educational institutions should operate under the assumption that a breach will occur by preparing to function even when essential networks go offline. This preparation involves discussing alternative workflows for attendance or medical software, or actively simulating attacks by turning off specific systems during the school year or summer.
Steinhauer told the editorial board that conducting tabletop simulations represents a premier strategy for these organizations to comprehend the impacts of single or multiple system failures and determine methods for maintaining ongoing operations.
Contingency planning costs very little and helps schools identify weaknesses before a real crisis hits. However, drills alone will not solve every threat. Districts still need to strengthen foundational safeguards, including tracking all software in use, teaching cybersecurity practices to students and teachers, and requiring strong passwords alongside two-factor authentication.
Even with strict safeguards in place, sensitive data can still be lost, and well-resourced schools remain vulnerable to sophisticated hacks. As state districts confront the reality that they cannot completely keep attackers out, planning ahead remains their best defense to keep students in classrooms.
Related reading
- UAlbany Study Finds Regulatory Barriers Limit Dental Hygiene Access
- UAlbany Study Says Regulatory Barriers Limit Dental Hygiene Access
- Releasing Updates for Sixteen Security Flaws on November 12, 2026 (archyde.com)
- Thousands of hoax bomb alerts sent to schools in Italy, U.K. and Ireland (newsarchyuk.com)
UAlbany Study Finds Regulatory Barriers Limit Dental Hygiene Access
State laws and regulations governing dental hygienists can limit where and how they practice, restricting patient access to...
UAlbany Study Says Regulatory Barriers Limit Dental Hygiene Access
State laws restricting dental hygienists from practicing independently limit preventive care access for underserved communities, according to a...

North Dakota Secures $206 Million for Rural Health Transformation
A joint statement released by the state's three federal delegates revealed that North Dakota is set to secure...
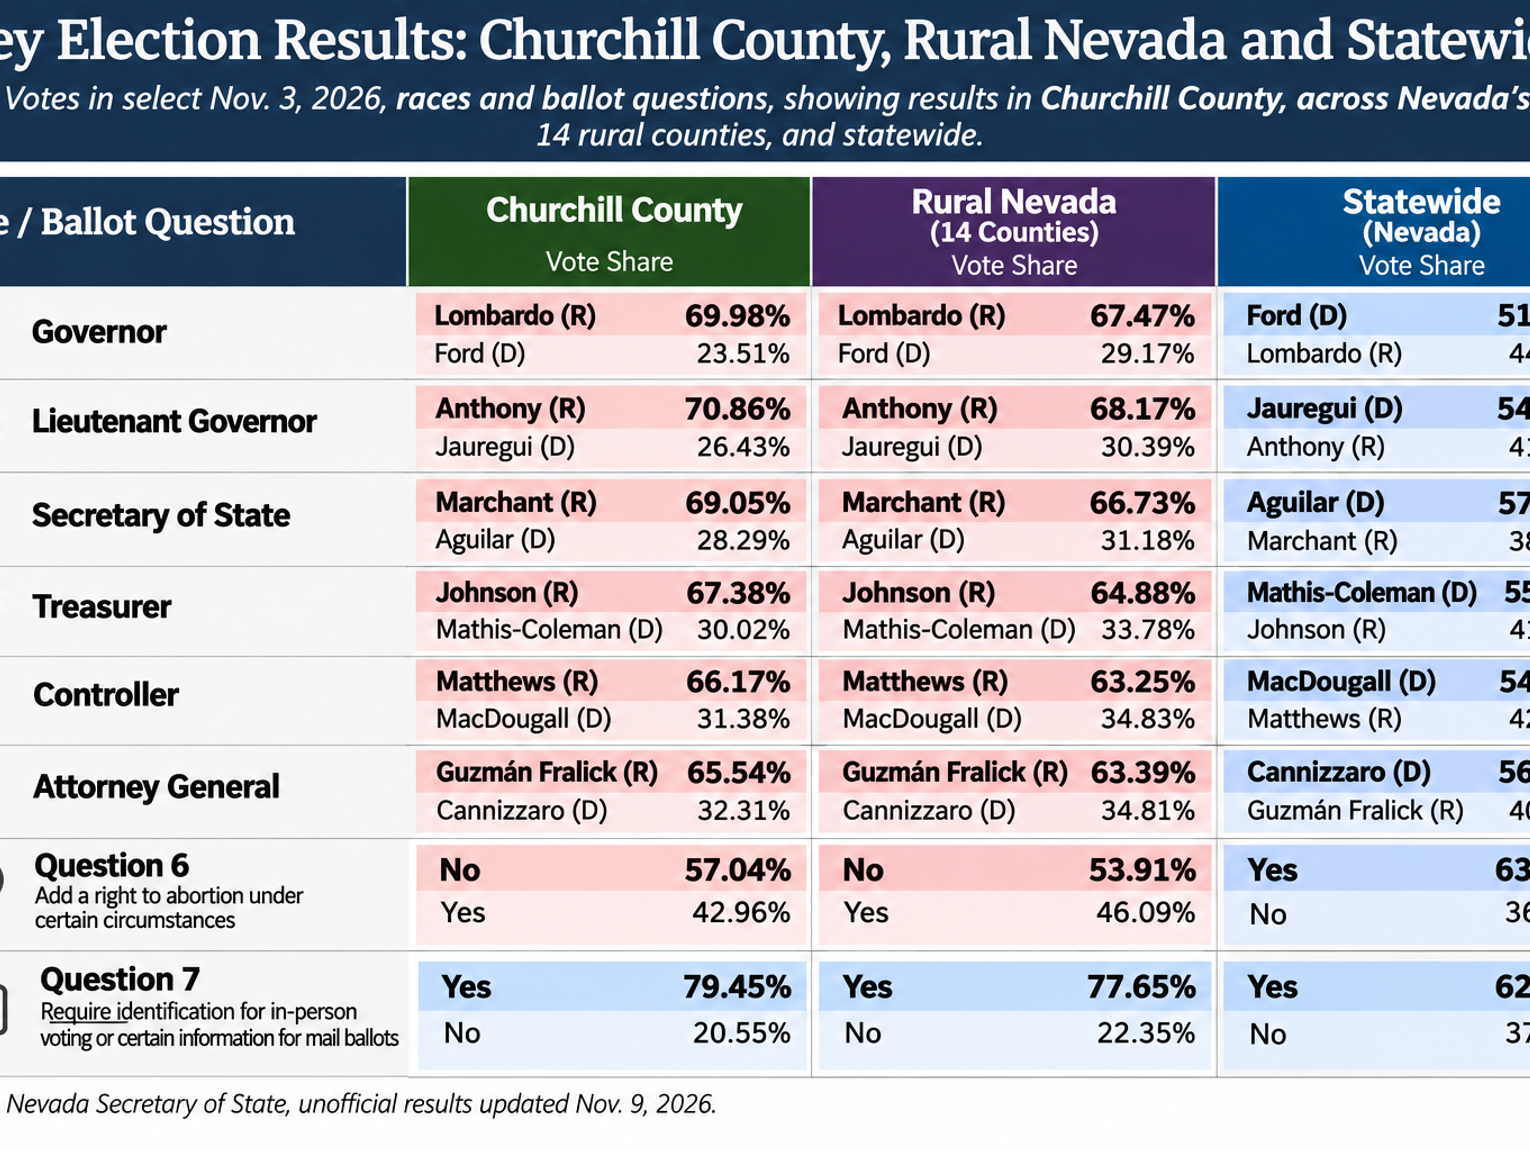
Churchill County Voters Split From Statewide Election Results – The Fallon Post
Churchill County voters broke sharply from statewide trends in the November 3 general election, favoring Republican candidates even...